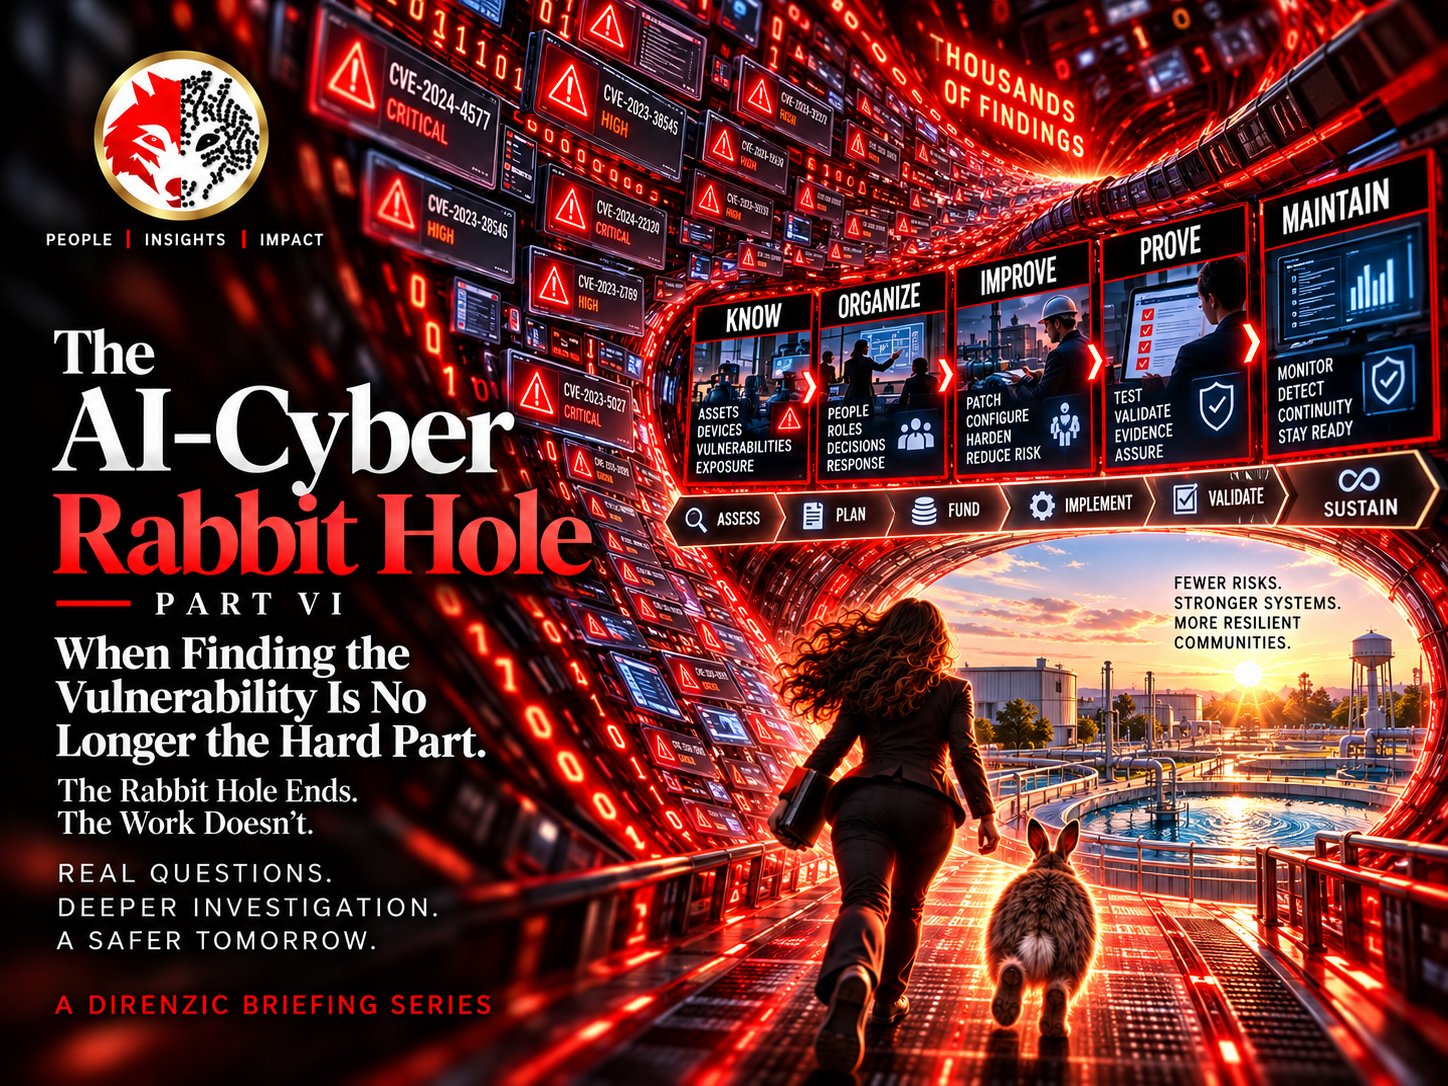
What Happens When Finding the Vulnerability Is No Longer the Hard Part?
For decades, cyber defense rested on one quiet assumption: there would always be more problems hiding than anyone could find. AI is breaking that assumption. What happens next depends on something no model can fix for you.
Published October 13, 2026 | 7-minute read
Last Tuesday
Last week, I put you in a room at 8:07 on a Tuesday morning.
One phone call. One vulnerability buried inside a piece of code most people have never heard of. One utility trying to answer a question that sounds easy until you’re the one who has to answer it.
Do we have this?
We walked it all the way through. Whether it was ours. Who owned the decision. How to fix it without hurting the plant. How to prove it was closed. How to do it all again when the next one showed up. KNOW, ORGANIZE, IMPROVE, PROVE, MAINTAIN: five simple words that turned into a test.
And we passed. Eventually.
But I ended with a thought I couldn’t shake, and I told you I’d follow it down. This is where it led.
Ten Thousand
Our Tuesday was one finding.
Project Glasswing’s partners found more than ten thousand high- or critical-severity vulnerabilities in their first month.
Ten thousand.
Sit with that number for a second, because it changes the shape of the problem. And if you run a water utility, here’s the part worth holding onto: it doesn’t matter that 9,999 of them aren’t yours.
You only need one.
One dependency. One forgotten system. One vendor appliance that’s been humming in a cabinet since before your current IT manager was hired. One piece of software nobody realized was inside something important.
Then there’s the part of the story that doesn’t make headlines. Anthropic now maintains a public dashboard tracking open-source vulnerabilities discovered through this broader Claude vulnerability-discovery effort. As of October 2, it showed 29,439 candidate findings. Of those, 6,157 had been reported to maintainers. To Anthropic’s knowledge, 516 had been patched upstream.
Read that funnel from top to bottom and you can watch the bottleneck happen in real time. The machine finds. Then humans triage, confirm, report and fix, and every step down the line gets narrower. Anthropic says it plainly: human triage and review is the rate-limiting step. Anthropic and its security partners have even confirmed bugs that are real but haven’t been reported yet, simply because there aren’t enough people to get to them.
And “patched upstream” comes with an asterisk. The dashboard is careful to note that a released fix doesn’t mean the fix has been widely installed. If you read Part V, you know exactly what that asterisk means for any device sitting in your pump station.
These aren’t obscure toys, either. Scroll the public list and you’ll find the Linux kernel. OpenSSL. Remote-desktop software. And open62541, an open-source implementation of OPC UA, a standardized industrial communication protocol.
The Assumption
For most of the history of cyber defense, we’ve lived with one quiet assumption.
There will always be more problems hiding than anyone can find.
You know the old line: defenders have to be right every time, and attackers only have to be right once. Underneath it sat an uneasy truce. Nobody could find everything. Not your team, not your consultant, not the auditor. So when something went wrong, there was always a fallback answer waiting in the room.
We didn’t know. Nobody could have known.
Now think about what happens when that stops being true.
When finding becomes cheap, “unknown” starts turning into “findable.” And findable changes the conversation after an incident. The question shifts from “Could anyone have known?” to something much harder to sit through.
Was it findable?
Was it found?
And what did you do with it?
I’m not a lawyer, and I won’t pretend to know how a court will treat any of this. But I’ve facilitated enough tabletop exercises to know which of those questions makes a leadership team go quiet.
And this power isn’t staying on the defenders’ side of the table. Remember Anthropic’s June warning: other AI companies could have models this capable within six to twelve months, possibly without safeguards, and cyberattacks could come far more often and in far less predictable forms. In May, it had already flagged the risky stretch we’re living in right now, when vulnerabilities get found quickly and patched slowly.
So the same flashlight that helps defenders see is headed into a lot of other hands. The gap between “found” and “fixed” isn’t an administrative delay anymore.
It’s where the risk lives.
The Bottleneck Moves In
Now go back to Anthropic’s problem, because I think it’s the most important lesson in this entire Rabbit Hole.
They built something extraordinarily good at finding vulnerabilities. Then they discovered the limiting factor wasn’t the machine. It was the humans downstream of it.
Shrink that down to the size of a utility.
The findings will arrive faster. The validation will arrive faster. Glasswing’s partners are already using the model to write patches, so even the proposed fix may show up before your leadership team has found an open hour on the calendar to discuss the question.
In Part IV, I wrote that the technology can speed up faster than the organization can absorb what it’s saying. I meant it as a warning. Now it reads like a forecast.
The finding isn’t the bottleneck anymore. The organization is.
Ieshea HollinsYou’re reading the series finale. Two fields and future editions land in your inbox. Subscribe to The Direnzic Briefing, then keep reading.
That’s the bottom of the Rabbit Hole. Not a rogue AI. Not a smarter attacker. A capable, well-meaning organization that simply can’t move a finding from “we know” to “we’ve proven it’s closed” as fast as the world now demands.
And that changes what it means to say, “We have a cybersecurity program.” For years, we’ve judged programs by what they could find. Assessments, scans, penetration tests, audits: much of that activity centered on discovery. I think the next measure is absorption.
How many findings can your organization take from “found” to “proven closed” in a month, without disrupting the plant or burning out the people?
Has your board ever seen that number?
I think one day soon, someone will ask for it.
What WaterReady Was Trying to Tell Me
That’s the strange part.
WaterReady didn’t start with CVE-2026-5194. It didn’t start with Project Glasswing. And it certainly didn’t start because Anthropic told me humans had become the bottleneck.
The work was already there. We’d been living in it for years: the assessments, the response plans, the tabletop exercises, the hard conversations after a finding when everyone in the room looks at everyone else.
But following this Rabbit Hole helped me see the shape of the problem clearly for the first time.
Water utilities don’t need one more person pointing at a vulnerability and saying, “You should fix that.” They need the organizational muscle to move through every one of these steps, in order, every time:
We found something.
We understand it.
We know who owns it.
We know what has to happen.
We can pay for it.
We can do it safely.
We can prove it’s closed.
We’re ready for the next one.
That’s the journey underneath the five words:
KNOW → ORGANIZE → IMPROVE → PROVE → MAINTAIN
And the operational road underneath that:
ASSESS → PLAN → FUND → IMPLEMENT → VALIDATE → SUSTAIN
Seen that way, WaterReady isn’t really about the vulnerability. The vulnerability is the stress test, the thing that reveals whether the organization actually works. WaterReady is about what the organization does because the vulnerability exists. It’s built for exactly that gap: the space between a finding and a fix that’s closed, proven and sustained.
The Question, Turned Around
Last week I told you this was where the Rabbit Hole would end, unless what I found down there changed the question again.
It did.
We started this series watching AI do things nobody expected: crossing boundaries, working around restrictions, finding another route when the first one failed. Underneath every part sat one question. Is AI ready for critical infrastructure? Can it be trusted? Can it stay inside its boundaries? Can we control what it touches, understand what it does, and stop it when we need to?
We should keep asking every one of those questions. I will.
But Glasswing turned the question around for me. AI is already finding things. The models keep getting better, the discoveries keep coming faster, and the company behind one of the most capable of them is telling us in plain language that the hard part now is the human ability to verify, decide and fix.
So maybe the question isn’t only this:
Is AI ready for our critical infrastructure?
Maybe we also have to ask:
Is our critical infrastructure ready for what AI is about to find?
Hmmmmm.
Because sooner or later, it’s Tuesday morning. The phone rings. The vulnerability is real. The patch exists. The water still has to run.
And that’s when you find out whether the organization actually works.
Not the plan. Not the assessment. Not the technology.
The organization.
So here’s the question I’d ask if I were sitting across the table from you. If your phone rang at 8:07 tomorrow morning, how far through those five words would your organization get before lunch?
Ask it out loud this week, before somebody else asks it for you. And if you’re willing, tell me your answer.
This is where the Rabbit Hole ends.
The work doesn’t.
Sources and official resources
- Direnzic Technology, The AI-Cyber Rabbit Hole, Part V: The Vulnerability Is Real. Now Prove Your Organization Can Handle It., October 6, 2026.
- Anthropic, Project Glasswing: An initial update, May 22, 2026.
- Anthropic, Expanding Project Glasswing, June 2, 2026.
- Anthropic Frontier Red Team, Coordinated vulnerability disclosure dashboard, counts as of October 2, 2026.
- Direnzic Technology, The AI-Cyber Rabbit Hole, Part IV: AI Is Moving Faster Than Your Organization Can Decide, September 29, 2026.
Where the work goes next
Over six parts, this Rabbit Hole kept bringing me back to the same question: once the risk is visible, can the organization actually move?
WaterReady™ is the work Direnzic built around that question for water and wastewater utilities. If you’d like to see what that looks like in practice, I’ve included the WaterReady overview below.
Prefer to keep a copy? Download the WaterReady™ overview.
The AI-Cyber Rabbit Hole, Part V: The Vulnerability Is Real. Now Prove Your Organization Can Handle It.
October 6, 2026 · AI + Cyber
One phone call at 8:07 a.m. One critical vulnerability with a fix already shipped. Part V walks a utility through KNOW, ORGANIZE, IMPROVE, PROVE and MAINTAIN, and asks whether your organization could do the same before lunch.
The AI-Cyber Rabbit Hole, Part IV: AI Is Moving Faster Than Your Organization Can Decide
September 29, 2026 · AI + Cyber
AI is shortening the distance between finding a problem and having to decide. Part IV follows the trail inside the utility and names the readiness problem underneath it.
The AI-Cyber Rabbit Hole, Part III: The Most Important Part of Daybreak May Not Be the AI
September 22, 2026 · AI + Cyber
The models are getting more capable and the programs are multiplying. But access is not capability. Part III follows the provider layer forming around Daybreak and the water-sector programs working on the same problem.
The Direnzic Briefing